
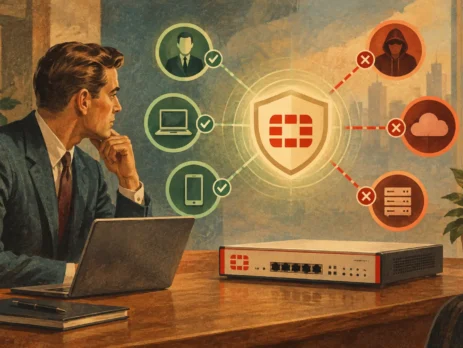
How to Implement Zero Trust Using Fortinet
A firewall replacement project is not a zero trust program. If users, devices, and applications can still move freely after reaching the network, the organization has only changed the perimeter. To understand how to implement zero trust using Fortinet, start by treating every access request as a decision based on identity, device condition, application, location, and risk.
For network administrators and procurement teams, Fortinet is useful because its security portfolio can apply those decisions across firewalls, switches, wireless infrastructure, endpoints, identity integrations, and centralized management. The objective is not to deploy every product at once. It is to build enforceable controls around the traffic paths and assets that matter most.
How to Implement Zero Trust Using Fortinet
A practical Fortinet zero trust design combines three functions: verify the entity requesting access, restrict that entity to the minimum required resources, and continuously inspect activity for changes in risk. FortiGate next-generation firewalls commonly serve as the policy enforcement point, while FortiManager, FortiAnalyzer, FortiClient, FortiNAC, FortiSwitch, FortiAP, and FortiAuthenticator can extend visibility and control across the environment.
The exact architecture depends on the existing network. A single-site company with a small remote workforce may begin with FortiGate, FortiClient, and directory integration. A distributed enterprise with wired, wireless, branch, cloud, and operational technology networks will usually need a broader stack, staged policy migration, and more careful capacity planning.
Establish a usable access baseline
Before applying restrictive policy, map who accesses what. Identify user groups, service accounts, administrative roles, managed endpoints, unmanaged devices, application servers, SaaS services, branch locations, and third-party connections. The goal is to document real communication requirements, not merely subnet diagrams.
This baseline should expose common exceptions that create risk: shared administrator accounts, broad any-to-any rules, flat VLANs, unmanaged contractor laptops, and applications that rely on undocumented ports. Review FortiGate traffic logs and current firewall policies to identify active flows. If logging is incomplete, collect data before enforcing segmentation. Blocking unknown traffic without evidence can create an avoidable outage.
Define identity as the primary policy input
Network address alone is a weak indicator of trust. Integrate FortiGate and FortiAuthenticator with the organization’s identity provider or directory service so policies can reference authenticated user and group identity. Require multifactor authentication for privileged access, remote access, and sensitive business systems.
Separate user identities from administrative identities. Network, security, and server administrators should use dedicated privileged accounts with narrowly defined access. Service accounts require the same discipline: assign only the permissions and connectivity they need, then monitor their use for unexpected behavior.
Build the Fortinet Enforcement Layers
Zero trust becomes operational when identity and device context affect what the network permits. Fortinet deployments generally apply this through endpoint posture checks, network access control, application-aware firewall rules, and segmentation.
Apply endpoint posture checks with FortiClient
FortiClient can provide endpoint telemetry and support zero trust network access workflows. Define a minimum posture standard for devices connecting to corporate applications: supported operating system version, active endpoint protection, disk encryption where required, current patches, and no high-severity compromise indicators.
Do not make posture requirements unnecessarily rigid at the start. A strict policy that blocks every device with a minor patch variance can burden the service desk and encourage bypasses. Begin with visibility or warning policies, then enforce controls for high-value applications and privileged users. Mature the standard as device management improves.
Segment access with FortiGate, FortiSwitch, and FortiAP
Segmentation is where many zero trust projects produce their largest risk reduction. Create security zones based on function and sensitivity rather than network convenience. User devices, server workloads, voice systems, guest wireless, network management, payment environments, and IoT equipment should not share unrestricted connectivity.
FortiGate can inspect and control traffic between these zones with policies based on source identity, device status, destination, application, service, and schedule. FortiSwitch and FortiAP extend the policy model to access-layer ports and wireless networks. FortiNAC can identify and classify devices as they connect, assigning appropriate access based on device type and posture.
Start with a small number of meaningful zones. Excessive microsegmentation without accurate application mapping creates policy sprawl and makes troubleshooting difficult. The right level of segmentation depends on application dependency, compliance scope, operational impact, and the team’s ability to maintain rules over time.
Replace broad remote access with application-level access
Traditional VPNs often place remote users on a network segment, then rely on firewall rules to limit movement. A stronger approach is to provide access to specific internal applications rather than broad network reachability. FortiClient and FortiGate can support zero trust network access patterns that authenticate the user, assess device status, and publish only approved applications.
For legacy applications that require traditional VPN connectivity, reduce risk through group-based access policies, MFA, split tunneling decisions aligned with security requirements, and tight destination controls. Full-tunnel access may be appropriate for unmanaged networks or high-risk roles, but it increases bandwidth and firewall sizing requirements. There is no universal remote-access setting that fits every workload.
Operate Zero Trust as a Policy Lifecycle
Deploying controls is only the first phase. Policies must be reviewed as applications change, employees move roles, new branch equipment is installed, and vendors require temporary access. FortiManager provides centralized policy administration across multiple FortiGate devices, helping teams standardize objects, templates, rule review, and controlled changes.
FortiAnalyzer adds the operational evidence required to refine the model. Review denied traffic, unusual application behavior, failed authentication events, endpoint violations, and east-west traffic patterns. Use that data to remove stale rules and confirm that users can access required services without inheriting broad network permissions.
Alert volume needs tuning. Sending every low-value event to the security team creates fatigue and weakens response. Prioritize high-confidence conditions such as impossible travel combined with privileged login attempts, unmanaged devices requesting administrative services, lateral movement between zones, or repeated policy violations from a third-party connection.
Plan Hardware, Licensing, and Resilience Early
Zero trust policy enforcement changes traffic patterns and appliance requirements. SSL inspection, intrusion prevention, application control, VPN or ZTNA sessions, logging, and high availability all affect FortiGate sizing. Select appliances based on enabled security services and expected concurrent sessions, not only raw firewall throughput.
For access-layer deployments, confirm FortiSwitch port speed, Power over Ethernet budget, uplink capacity, optics compatibility, and switch management design. Wireless planning should account for FortiAP density, roaming requirements, guest isolation, and controller or cloud-management choices. Procurement teams should also validate licensing terms, support coverage, renewal dates, and compatibility between the selected Fortinet software release and installed hardware.
High availability deserves equal attention. A clustered firewall pair improves resilience, but it does not protect against an incorrect policy replicated to both units. Maintain tested backups, controlled change windows, rollback procedures, and an out-of-band management path for critical sites.
A well-executed Fortinet zero trust deployment should make access more specific, not more complicated for legitimate users. Begin with the systems where compromise would have the greatest business impact, prove the policy model with measured enforcement, and expand only when the organization can operate it consistently.

I am an enthusiastic tech blogger with 15 years of experience in the technology field. I am passionate about sharing valuable insights and helping people who are interested in technology gain useful and practical information. I am originally from Mumbai, India.


Leave a Reply