
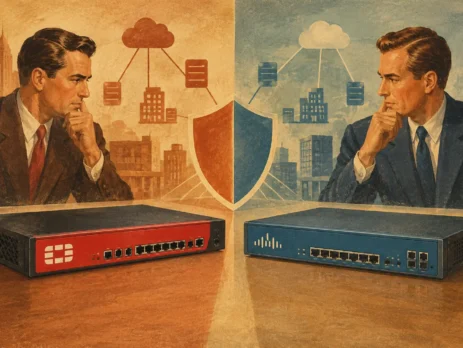
FortiGate Versus Cisco Firewall for Enterprises
A firewall refresh rarely starts with a feature checklist. It starts when a branch appliance reaches end of support, remote access performance becomes inconsistent, or a security team needs better visibility without adding another management console. The FortiGate versus Cisco firewall decision should therefore be based on the operating model, traffic profile, licensing plan, and installed network environment – not simply on brand preference.
For enterprise buyers, both vendors offer capable next-generation firewall platforms. The meaningful differences appear in how each platform processes encrypted traffic, applies threat inspection, integrates with surrounding security tools, and fits into a multiyear hardware and support lifecycle.
FortiGate Versus Cisco Firewall: The Core Difference
FortiGate appliances are built around Fortinet’s Security Processing Units, or SPUs. These purpose-built ASICs accelerate firewall, VPN, and security inspection functions, allowing many FortiGate models to deliver strong price-to-performance results for branch, campus edge, and distributed enterprise deployments. FortiOS provides the operating system and security feature set across the product family, which can simplify standardization between small sites and data center environments.
Cisco’s firewall portfolio requires more careful definition. For a direct next-generation firewall comparison, Cisco Secure Firewall running Secure Firewall Threat Defense is the relevant platform. It combines stateful firewall controls with intrusion prevention, malware defense, URL filtering, and application visibility. Older Cisco ASA platforms remain widely deployed, particularly where stable VPN, segmentation, or legacy policy requirements are the priority, but ASA and Secure Firewall Threat Defense should not be treated as identical products.
Cisco also offers Meraki MX appliances. These are often suitable for cloud-managed branch deployments, but they serve a different operational and feature model than Cisco Secure Firewall. Procurement teams should avoid comparing a Meraki MX specification sheet directly against a FortiGate model intended for deeper next-generation inspection.
The practical distinction is straightforward: FortiGate commonly appeals to organizations seeking high inspected throughput, integrated security functions, and consolidated branch protection. Cisco Secure Firewall commonly appeals to organizations that already depend on Cisco security architecture, Cisco identity controls, or Cisco-centric operations and want those systems to work together under established policies.
Performance Must Be Measured Under Inspection
Published firewall throughput can be misleading if it is used as the only sizing metric. A device may show a high stateful firewall rating while delivering substantially lower performance with IPS, application control, malware inspection, SSL/TLS decryption, logging, and VPN services enabled. Those are the workloads that matter in a production security design.
FortiGate’s ASIC architecture is a major consideration here. Hardware acceleration can provide an advantage where organizations need to inspect high volumes of traffic while controlling appliance cost, rack space, and power use. This is particularly relevant for internet-facing branches, SD-WAN hubs, distributed retail locations, and environments where encrypted traffic inspection is expected to grow.
Cisco Secure Firewall sizing should focus on the exact Threat Defense feature set to be enabled. Cisco offers substantial capability, but effective performance planning requires realistic assumptions about concurrent sessions, encrypted traffic ratios, remote-access users, east-west segmentation, and logging volume. A model selected only for nominal throughput can become constrained after policy expansion or a move toward broader decryption.
For either vendor, ask for measurements that reflect the intended configuration: threat inspection enabled, TLS decryption enabled where policy permits, expected VPN usage, and high-availability operation. A firewall should retain sufficient headroom for new applications, security signature growth, and traffic increases over its useful life.
Security Controls and Detection Strategy
FortiGate provides a broad integrated set of controls through FortiOS, including firewall policy, IPS, antivirus, web filtering, application control, VPN, SD-WAN, and network access functions. Organizations using Fortinet’s wider Security Fabric may also connect FortiGate appliances with switches, wireless access points, endpoint tools, analyzers, and centralized management products. The value is operational consolidation: fewer separate control planes for teams that prefer one vendor ecosystem.
Cisco Secure Firewall places significant weight on threat intelligence, intrusion prevention, and integration with Cisco security products. Cisco Talos intelligence and Snort-based inspection are relevant strengths for organizations that place a premium on mature threat research and detailed detection policies. Cisco environments may also benefit from integrations involving identity, endpoint telemetry, secure access, and security analytics.
Neither approach is automatically superior. A FortiGate can be the better fit when the goal is to combine multiple network security functions on a cost-efficient appliance. Cisco may be the stronger choice when firewall events need to feed established Cisco security workflows or when security staff already have experience tuning Cisco policies and investigating Cisco-generated telemetry.
The deciding question is not which vendor has more features. It is which capabilities the organization can consistently operate. Features that are not licensed, configured, monitored, and reviewed do not reduce risk.
Management and Daily Operations
Operational preference is often the factor that remains after performance requirements are met. FortiGate can be managed locally or through centralized Fortinet platforms, depending on deployment scale and governance requirements. Teams that support many similar branches often value consistent policy templates and the ability to standardize appliance families across locations.
Cisco Secure Firewall management may involve local tools for smaller use cases or centralized management for more complex deployments. Larger environments commonly need centralized policy control, event review, role-based administration, audit visibility, and coordinated software management. That is appropriate for enterprise security teams, but buyers should account for the management infrastructure, skills, and licensing associated with the selected model.
Change control deserves particular attention. Evaluate how each vendor handles policy objects, access rules, network address translation, VPN configuration, logging retention, software upgrades, rollback procedures, and high-availability failover. A platform can look efficient in a proof of concept yet become difficult to operate when hundreds of policies, multiple business units, and strict approval processes are involved.
Licensing, Support, and Lifecycle Costs
The appliance purchase price is only one part of the firewall budget. Most next-generation security functions require active subscriptions, and support coverage determines access to software updates, replacement service, and technical assistance. Compare the total cost across the intended ownership period rather than comparing hardware pricing alone.
FortiGate purchases typically need an assessment of security service bundles, support level, centralized management requirements, and any SD-WAN or cloud logging components. Cisco Secure Firewall purchases require the same discipline, with close attention to the licenses associated with Threat Defense features, management, analytics, and support entitlement.
License expiration does not usually mean that a firewall stops passing basic traffic, but it can materially reduce the protection expected from a next-generation deployment. Without current threat intelligence, signature updates, web categorization, malware analysis, or vendor support, the security posture changes. Procurement documentation should identify renewal dates, licensing terms, serial-number requirements, and responsibility for renewal management.
Hardware lifecycle matters as well. Exact model availability, software compatibility, rail kits, power supplies, transceivers, replacement fans, and support status can affect the viability of a deployment. This is especially relevant when expanding existing clusters or replacing a failed unit quickly. Suppliers such as Gear Net Technologies can assist buyers that need model-specific sourcing, including legacy or expansion hardware, but the organization should still validate entitlement transfer and vendor support eligibility before purchase.
When FortiGate Is Usually the Better Fit
FortiGate is often well suited to organizations that need strong security performance per dollar across many sites. It is a practical candidate for SD-WAN consolidation, branch firewall standardization, encrypted traffic inspection, and deployments where network and security teams prefer an integrated platform. It can also be attractive when the organization plans to extend the same vendor ecosystem into switching, wireless, centralized management, or security analytics.
That does not mean every FortiGate deployment is simple. Larger estates still require careful policy design, log storage planning, segmentation standards, and disciplined software lifecycle management. The benefit comes from selecting the correct platform and operating it consistently.
When Cisco Firewall Is Usually the Better Fit
Cisco Secure Firewall is often the logical choice where Cisco security tooling, Cisco-trained operations teams, and existing identity or endpoint investments already shape the architecture. Organizations with detailed governance requirements may value its security ecosystem integration and established detection capabilities. It can also reduce operational friction where the security operations center already uses Cisco workflows for investigation and incident response.
Cisco is less compelling if its surrounding ecosystem will not be used and the buyer is paying for complexity that the team does not need. A smaller distributed organization may find that a more consolidated platform better matches its resources, especially when branch performance and straightforward administration are the main requirements.
Make the Selection From a Tested Design
The best firewall is the one sized for actual inspected traffic, supported by current licenses, manageable by the assigned team, and available with a replacement plan. Build the evaluation around a representative policy set, realistic decryption requirements, VPN demand, log retention, and the systems the firewall must integrate with. That process turns a FortiGate versus Cisco firewall comparison from a brand debate into an infrastructure decision that can hold up through the next hardware cycle.

I am an enthusiastic tech blogger with 15 years of experience in the technology field. I am passionate about sharing valuable insights and helping people who are interested in technology gain useful and practical information. I am originally from Mumbai, India.


Leave a Reply